Barracuda NextGen Control Center for Amazon Web Services
Central Management of the Entire Enterprise Security Infrastructure
List Price:
Our Price: $3,420.00
List Price:
Our Price: $14,136.00
 Overview:
Security-conscious companies and managed security providers are confronted with an increasing number of gateways in their networks. Managing hundreds or thousands of systems can require a costly, timeintensive process by qualified staff. The Barracuda NextGen Control Center can significantly decrease administrative overhead.
Moving your IT Infrastructure to the Cloud? Running on Amazon Web Services?
Barracuda Networks is your partner for various kinds of deployments in Amazon Web Services. We understand your IT needs and provide best-of-breed solutions for firewalling, load balancing, web application security, and email security in the public cloud.
Barracuda Networks and Amazon Web Services
Today, many organizations are looking to the cloud to take advantage of the economic gains and operational efficiencies inherent to non-hardware-based solutions. While migrating to the cloud means companies need to adjust to new security threats, the ability to scale according to business needs means that AWS offers a powerful value proposition. The pay-as-you go model Amazon uses enables businesses of all sizes to access just the AWS services they need, and no more.
In the cloud, companies need security that can compensate for a broader attack surface and a new array of threat vectors. As Amazon seeks to provide more options for hybrid cloud and pay-as-you-go subscriptions, Barracuda’s security services have moved hand-in-hand with Amazon’s values. Not only is Barracuda committed to providing total threat protection to AWS customers, but we’re taking steps to emulate Amazon’s methodologies within our product offerings. Barracuda and Amazon work well together because we have the same end user in mind: A person Amazon calls the “whole stack professional” and Barracuda describes as a “mid-market IT professional who wears a lot of hats.”
Move Your Physical Data Center to the Cloud with Amazon Web Services
Get Secure Connectivity with Visibility and Control by using the industry's most advanced next-generation firewall solution for deployments in Amazon Web Services. The Barracuda NextGen Control Center ensures highly secure, encrypted traffic from, to, and within AWS, provides secure remote and site-to-site access, and centralized management.
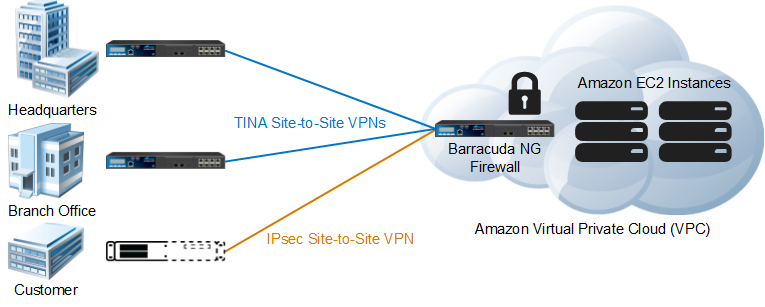
The growth in cloud computing capabilities and services has driven more data into places where traditional IT security measures cannot reach - into data centers not owned by your corporate IT group. Securing applications and data in AWS is far easier with tools that are dedicated to the task. Deploying the Barracuda NextGen Control Center in the cloud is very similar to running local network firewalls, and provides the advantages of common policy enforcement and distributed security management in a hybrid-IT environment. It provides next generation firewalling and secure remote access to AWS. It enables organizations to deploy sophisticated multi-zone network architecture in the cloud, just like their on-premises networks. By using the proprietary high-performance VPN protocol extension TINA (Transport Independent Network Architecture), the Barracuda NextGen Control Center deployment enables secure high speed site-to-site and client-to-site connectivity between on-premises networks and mobile-user devices. The Barracuda NextGen Control Center adds a powerful and intuitive centralized management portal that makes it extremely simple to deploy, configure, update, and manage multiple units from a single location, while also providing comprehensive, real-time network visibility and reporting.
The Barracuda Advantage
- Increased security and reduced costs
- Revision capabilities and easy restoration of proven configurations
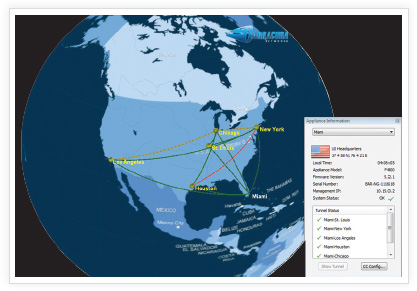
- Simple drag & drop configuration and visualization of VPN tunnels
- Fully scalable to grow with organizational needs and requirements
- Disaster recovery within a few minutes using only two configuration files
Product Spotlight
- Powerful, scalable, industry-leading central management
- Comprehensive revision control system
- Consistent security posture and policy enforcement across the entire enterprise
- Integrated Public Key Infrastructure (PKI)
Cost EfficiencyThe Barracuda NextGen Control Center gives full control over system administration costs. Lifecycle costs: Central update management drastically lowers the time spent deploying patches. Even Barracuda CloudGen Firewalls, with different software versions can be centrally managed at the same time. |
|
Security Management with EaseFirewall rulesets and other security policies, as well as, software patches and version upgrades are centrally controlled from within the management console. Deployment can be scheduled and applied to all managed devices. Highly customizable administrative roles allow delegation of administrative capabilities for specific departments or locations. Administrators are kept informed at all times on the status of remote gateways and can implement centrally defined security rules at every location. Furthermore, the integrated revision control system provides easy audits and cuts overhead.
|
Deployment:
The Barracuda NextGen Control Center can run as a virtual appliance in the Amazon cloud as a gateway device for Amazon EC2 instances in an Amazon Virtual Private Cloud (VPC).
Follow the steps in this article to deploy the Barracuda NextGen Control Center in an Amazon VPC.
Model Comparison:
| Model Comparison | VCC400 | VCC610 |
|---|---|---|
| Max. no. of Managed Gateways (Recommended) | Not limited (20) | Not limited (depending on compute instance) |
| Manageable Configuration Groupings | 1 | Not limited |
| Multi-Administrator Support | ||
| Role-based Administration | ||
| Revision Control System | ||
| Central Statistics | ||
| Central Syslog Host / Relay | ||
| Firewall Audit Information Collector / Viewer | ||
| Barracuda Access Monitor | ||
| Barracuda Earth | ||
| PKI Service | ||
| Multi tenancy | Yes (via configuration groupings) |
Technical Specs

Configuration Management
- Multitenant capabilities
- Configuration templates
- Object database and template repository
- Firewall/VPN policies, application gateway parameters
- Flat file data storage
- Database characteristics (transaction, orientation, locking, etc.)
- Easy configuration backup & restore
- Speed install support via USB key
- Configuration update monitoring
- Full RCS versioning
- VPN graphical tunnel interface
- Barracuda Networks Access Client policy management
- Multi-release management
- Multi-platform management

Status Monitoring
- Gateway health state
- Launch pad functionality
- Customizable layout
- Barracuda Earth support

Trust Center
- Gateway x.509 certificate CA
- Gateway SSH key management
- VPN server for management tunnels
- Virtual IP addresses for gateways
- Dynamic gateway IP address support

License Center
- License timestamp server
- License status display
- Central event message list
- Central event database
- Event forwarding (SNMP, mail)
- Event log

Central Session Tracking
- Administration Session display
- Administration Session termination

Central Software Update
- Real-time version display
- Kernel and OS updates
- Barracuda CloudGen Firewall F-Series updates
- Update log viewer

Secure Remote Execution (SSHv2)
- Job scheduling
- Script management
- Execution log viewer

Administration Models
- Fully GUI-based access
- Strong authentication & AES encryption
- Role-based administration
- Adjustable view on configuration tree
- Configurable administrative domains
- Multiple domains per administrator
- Configurable access notification

Reporting & Accounting
- Historical reports on gateway activity
- Customer-based gateway activity reports
- Policy distribution
- Control-Center resource utilization
- Gateway resource utilization
- Central log host
- Streaming/relaying to external log host

Additional Functions
- NTP4 time server for gateways
- Integrated DNS server
- High availability
- SIEM syslog interface
- Public Key Infrastructure
- Revision Control System
- Barracuda Access Monitor
Support Options

Barracuda Energize Updates
- Standard technical support
- Firmware updates
- IPS signature updates
- Application control definition updates
Documentation:
Download the Barracuda NextGen Control Center for Amazon Web Services Data Sheet (.PDF)
Pricing Notes:
- Pricing and product availability subject to change without notice.
List Price:
Our Price: $3,420.00
List Price:
Our Price: $14,136.00
List Price:
Our Price: $786.60
List Price:
Our Price: $3,420.00