Barracuda CloudGen Firewall VFC8
Scalable security for the homeoffice, Kiosks, and IoT/OT
Get a Quote!
Including Energize Update, Advance Threat Protection, and Firewall Insights
List Price:
Our Price: $9,405.00
Including Energize Update, Advance Threat Protection, Firewall Insights, Malware Protection, and Advance Remote Access
List Price:
Our Price: $11,628.00
Click here to jump to more pricing!
Barracuda CloudGen Firewall VFC:
Enterprise networks grow larger and more complex every day - and more critical to key business operations. The virtual appliance Barracuda CloudGen Firewall VFC is an essential tool to optimize the performance, security, and availability of today’s dispersed enterprise WANs.
Integrated Next-Generation Security
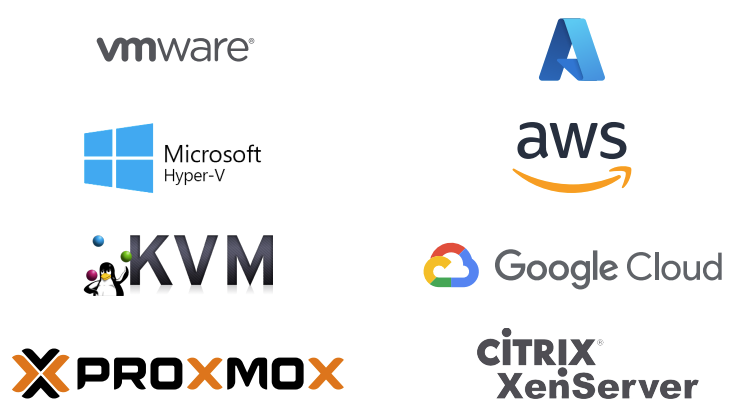
Barracuda CloudGen Firewall VFC is designed and built from the ground up to provide comprehensive, nextgeneration firewall capabilities. Based on application visibility, user-identity awareness, intrusion prevention, and centralized management, the CloudGen Firewall VFC is the ideal solution for today’s dynamic enterprises as it is fully compatible with VMware, XenServer, KVM, Proxmox, and Hyper-V virtualization.
Regaining Control of User Activity
Barracuda CloudGen Firewall VFC restores control to networks made opaque and unmanageable by mobile devices at work, Web 2.0 applications, increasing dispersion, and the growing integration and dependence on cloudbased resources. It extends security coverage beyond network boundaries, and makes it easy to monitor and regulate everything the network and its users are doing.
True Enterprise Readiness
Barracuda CloudGen Firewall VFC meets the enterprise requirements for massive scalability and efficient management across dispersed networks. Integrated WAN optimization and centralized management enable organizations to increase system availability while keeping administrative time and operation costs low.
Virtual appliances
As organizations have adopted virtualization for their server infrastructures, there has been a corresponding trend to extend the benefits of virtualization to the security layer. A CloudGen Firewall virtual appliance (VFC) provides the same powerful technology, comprehensive features, and easeof-use found in a CloudGen Firewall hardware appliance. It is ideally suited for organizations that are standardizing hardware platforms or deploying virtual environments.
Beyond its powerful network firewall, IPS, SD-WAN, and remote access technologies, CloudGen Firewall VFC integrates a comprehensive set of next-generation firewall technologies, including application control, availability, and traffic flow optimization across the wide area network, web filtering, antivirus, anti-spam, and network access control enforcement.
Benefits:
Edge computing
Many of today's applications rely on real-time processing and do not tolerate long latency times. As a result, more companies are investing in edge computing. Combined with artificial intelligence (AI), edge computing enables companies to innovate more quickly, to achieve or exceed their planned business results. Barracuda CloudGen Firewall provides your organization with the security and connectivity to run edge-computing apps at every remote location. The Barracuda Firewall Control Center provides full control over edge computing deployments across large numbers of distributed locations, as well as seamless monitoring and policy enforcement.
Protect your data, users, and workloads wherever they reside
Modern cyber threats such as ransomware and advanced persistent threats, targeted attacks, and zero-day threats, require progressively sophisticated defense techniques that balance accurate threat detection with fast response times. Barracuda CloudGen Firewall offers a comprehensive set of next-generation firewall technologies to ensure real-time network protection against a broad range of network threats, vulnerabilities, and exploits, including SQL injections, cross-site scripting, denial of service attacks, trojans, viruses, worms, spyware, and many more.
Barracuda’s firewalls can be deployed across multiple physical locations as well as in Microsoft Azure, AWS, and Google Cloud Platform.
Mitigate cyber-risks with Barracuda’s multi-layered security approach
The polymorphic nature of modern cyber-threats renders signature-based defense mechanisms inadequate. Comprehensive, reliable protection against advanced persistent threats requires a layered approach. Barracuda CloudGen Firewall provides multiple layers of detection including advanced threat signatures, behavioral and heuristic analysis, static code analysis, and finally comprehensive sandboxing, to provide accurate detection and in-depth protection against ransomware, malware, and other advanced cyber-attacks.
Stop zero-hour attacks with Barracuda Advanced Threat Protection
The core of Barracuda Advanced Threat Protection is a comprehensive full-emulation sandbox that will ‘detonate’ any attachment that is not conclusively analyzed by the preceding layers. Once a new threat is identified and a signature is created, the information is pushed to the pre-filtering layers. The next time the same threat attempts to enter your network, it will be blocked without the need for repeating the resource-intensive sandbox analysis. This ensures that sandboxing is used as efficiently as possible and without significantly impacting operations.
Stay ahead of new threats with Barracuda's global threat intelligence network
The Advanced Threat Protection service is connected to Barracuda’s global threat intelligence network to provide real-time protection from the latest threats. Barracuda collects threat data from millions of sources around the world across all threat vectors including network, email, website attacks, and web browser threats. Once a threat is identified the information is made available to all security solutions connected to the service, making your threat defense continuously better and more effective.
Simplify your security deployment in the cloud
Fully leverage the benefits of SaaS and public-cloud services and infrastructures with simple, automated deployment, configuration, and management. Purpose-built for dispersed networks and cloud environments, Barracuda CloudGen Firewall makes cloud deployment easy with templates, APIs, and deep integration with cloud native features. Effortlessly roll out hardware to remote sites that lack qualified IT personnel with Zero-Touch Deployment.
Connect multiple locations and clouds with our built-in SD-WAN
Barracuda CloudGen Firewall, which can be deployed on premises or in the cloud, includes advanced SD-WAN capabilities and supports connections to distributed sites, multiple clouds, and remote users. There is no need to purchase a separate SD-WAN to manage connectivity among many distributed locations.
Features:
Security
While traditional solutions usually detect network threats after they have breached the network by sending log notifications to the administrator, Barracuda Advanced Threat Protection (ATP) implements full system emulation, providing deep visibility into malware behavior. Files are checked against a cryptographic hash database that is constantly updated. In case the file is unknown, it is emulated in a virtual sandbox where malicious behavior can be discovered.
Barracuda ATP offers Administrators granular, file-type-based control including automatic quarantine and block-listing features to maintain the highest level of protection for an organization’s network.
Barracuda Advanced Threat Protection is an optional subscription.
Botnet and Spyware Protection guards against botnet infections by blocking access to malicious sites and servers, and detects potentially infected clients based on DNS Sinkholing technology. DNS Sinkholing blocks clients from accessing malicious domains by monitoring outbound DNS requests passing through the firewall. DNS requests to malicious domains are redirected to an internal sinkhole, thereby preventing data exfiltration and identifying the victim. Once an infected client is detected, it can be isolated automatically. An alert can also be created or reported by Barracuda Firewall Report Creator.
The Intrusion Detection and Prevention System (IDS/IPS) of Barracuda CloudGen Firewall strongly enhances network protection by providing complete and comprehensive real-time network protection against a broad range of network threats, vulnerabilities, exploits, and exposures in operating systems, applications, and databases preventing network attacks such as:
- SQL injections and arbitrary code executions
- Access control attempts and privilege escalations
- Cross-Site Scripting and buffer overflow
- Denial of Service (DoS) and Distributed Denial of Service (DDoS) attacks
- Directory traversal and probing and scanning attempts
- Backdoor attacks, Trojans, rootkits, viruses, worms, and spyware
Barracuda CloudGen Firewall provides advanced attack and threat protection features such as:
- Stream segmentation and packet anomaly protection
- TCP split handshake protection
- IP and RPC defragmentation
- FTP evasion protection
- URL and HTML decoding
As a result, Barracuda CloudGen Firewall is able to identify and block advanced evasion attempts and obfuscation techniques that are used by attackers to circumvent and trick traditional intrusion prevention systems.
As part of Barracuda Energize Updates subscription, automatic signature updates are delivered on a regular schedule or on an emergency basis to ensure that Barracuda CloudGen Firewall is constantly up-to-date. If the firewall unit is centrally managed, the updates are conveniently distributed by Barracuda Firewall Control Center.
In today’s world of omnipresent botnets, one of the main tasks of perimeter protection is to ensure ongoing availability of the network for legitimate requests and to detect and repel malicious denial of service attacks. With TCP SYN Flood Protection, Barracuda CloudGen Firewall effectively functions as a generic TCP proxy, forwarding only legitimate TCP traffic to the inside of the network.
Additionally, Barracuda CloudGen Firewall allows the definition of a rate limit that is applied to the maximum number of sessions per source address to be handled by the firewall. Packets arriving at a rate faster than allowed will simply be dropped. In a massive DDoS attack, the attackers may simply aim for saturating the link by transmitting vast numbers of UDP packets. The integrated environmental monitoring feature of Barracuda CloudGen Firewall diagnoses such conditions by link and target address monitoring. Once the response of a remote target address to regular ICMP probing fails, the system can be configured to activate different routes and uplinks (for example backup line, ISDN, xDSL). Using this feature, traffic will be unimpeded across unaffected lines and crucial site-to-site and site-to-Internet connectivity remains operational.
The Malware Protection built into Barracuda CloudGen Firewall shields the internal network from malicious content by scanning web content (HTTP and HTTPs), email (SMTP, POP3), and file transfers (FTP) via two fully integrated antivirus engines. Barracuda Malware protection is based on regular signature updates as well as advanced heuristics to detect malware or other potentially unwanted programs even before signatures are available. Barracuda Malware Protection covers viruses, worms, Trojans, malicious java applets, and programs using known exploits on PDF, picture and office documents, macro viruses, and many more, even when using stealth or morphing techniques for obfuscation.
All Barracuda CloudGen Firewall models can apply IPS, Virus Protection, Application Control, URL Filter and even Advanced Threat Protection to SSL encrypted web traffic using the standard ' trusted man-in-the-middle' approach. SSL Interception can be fine-tuned to exempt local networks, users/groups, URL Filter categories or custom defined domains from SSL Inspection.
Build layers of security around your data, devices, and users. Multiple security layers are necessary in order to provide the protection your organization needs. Barracuda XDR adds additional layers of protection for major attack surfaces such as email, endpoints, servers, firewalls, and cloud devices.
At the heart of every Barracuda CloudGen Firewall is a high performance stateful deep packet inspection engine examining the header as well as the data part of every passing packet. Malformed packets are disregarded, protecting the infrastructure behind the Barracuda device against network level attacks. Protocol compliant packages are then checked to match any of the defined firewall rules.
Once a data packet is opened up for inspection by the Firewall, all other security inspection mechanisms like IPS/IDS, anti-virus are also applied to the packet or stream of consecutive packets. Security inspection is done in single pas mode without the need to hand over to a separate proxy.
Multi-factor authentication (MFA) has become the standard for preventing unauthorized access to company critical information. Barracuda CloudGen Firewall supports and enforces multi factor authentication methods for protected resources, SSL-VPN as well as VPN connections. This makes the need for purchasing an additional multi-factor authentication or identity access management (IAM) solution obsolete.
Time-based one-time passwords (TOTP) are commonly used for two-factor authentication and is today the de-facto standard for multi factor authentication methods as used by cloud application providers. Every Barracuda CloudGen Firewall includes an advanced multi-factor authentication function using the TOTP algorithm to protect company critical resources as well as SSL-VPN and VPN connections from unauthorized use.
Connectivity & SD-WAN
If Dynamic Bandwidth & Latency Detection indicates the measured bandwidth of an uplink is not sufficient to sustain the minimally required business critical traffic (e.g., VoIP), Barracuda CloudGen Firewall automatically shifts sessions for non-business critical traffic to secondary links to free up bandwidth for critical traffic.
Barracuda CloudGen Firewall uses dynamic bandwidth and latency detection to automatically balance existing sessions inside logical VPN tunnels across all available uplinks. This real-time balancing optimizes network efficiency and bandwidth usage at any given moment.
A unique combination of next-generation security and adaptive WAN routing technology allows Barracuda CloudGen Firewall to dynamically assign available bandwidth, uplink, and routing information based not only on protocol, user, location, and content, but also on applications, application categories, and even web content categories. This keeps expensive, highly available lines free for business- and mission-critical applications, while significantly reducing response times and freeing up additional bandwidth.
Barracuda CloudGen Firewall combines a comprehensive set of advanced security features with capabilities that support the Software-Defined Wide-Area Network (SD-WAN). SD-WAN capabilities allow CloudGen Firewalls to create secure pathways across both multiple WAN connections and multiple carriers, without the involvement of typical high-management overhead. Advanced load sharing lets you use multiple WAN connections simultaneously and distribute encrypted VPN tunnels across multiple WAN connections. Built-in compression, caching, and WAN optimization technologies significantly increase your available bandwidth. These capabilities reduce your need for expensive leased lines, consolidate multiple security functions into a single device, and create a unified management framework — all of which results in significant cost savings for your organization.
In order to achieve the best possible user experience across the Wide Area Network, all Barracuda CloudGen Firewall models pro-actively measure the available bandwidths and latency between VPN endpoints. The results are directly available to the firewall policy engine to select the best suitable uplink per application or disqualify an uplink if the bandwidth or latency fall outside of acceptable limits.
Barracuda CloudGen Firewall copies packets and sends them simultaneously through the selected primary and secondary VPN transports. Both packet streams are reassembled at the other end of the logical VPN tunnel. This significantly reduces packet loss for applications like VoIP or video streaming. It also provides instant failover — with no packets dropped — in case one VPN transport of a logical VPN tunnel goes down.
In order to achieve the best possible user experience across your WAN, all Barracuda CloudGen Firewall models are able to detect available bandwidths and latency between VPN endpoints in real time. The firewall policy engine is able to dynamically select the most suitable uplink for each application, or to disqualify an uplink if bandwidth or latency is outside defined limits. In addition, if the measured bandwidth of an uplink is not sufficient to sustain business-critical traffic (e.g., VoIP), the CloudGen Firewall automatically shifts sessions for non-critical traffic to secondary links, to free up high-quality bandwidth for critical traffic.
Due to the limitations that come with standard IPsec connections, Barracuda Networks has created several powerful extensions to standard IPsec tunnel management. This core of Barracuda Firewall VPN Engine is called TINA (Transport Independent Network Architecture). The TINA protocol allows the use of TCP, UDP, and ESP for high speed VPN connections, which improves the VPN connectivity substantially by adding:
- Endpoint-to-Endpoint (not network-to-network) connectivity
- NAT friendliness
- Multiple physical transport paths for a logical tunnel
- Multiple tunnels between two locations
- HTTPS and SOCKS4/5 proxy compatibility
- Dynamic Address Support
- Tunnel heartbeat monitoring
Create highly reliable and secure site-to-site connections between on-premises firewalls (both hardware and virtual appliances). Site-to-site connectivity also includes public cloud offerings like Amazon Web Services and Microsoft Azure. But it is not just about maintaining static site-to-site VPN tunnels. Having a hub-and-spoke VPN setup allows you to create tunnels automatically and on-demand between connected nodes in order to avoid the hub turning into a bottleneck. You thereby ensure low latency connections for VoIP applications, for example. As soon as the connection is no longer required, the VPN tunnel is automatically closed again. Administrators naturally have full real-time visibility into the dynamic mesh VPN setup.
To ensure unbeatable, cost-efficient connectivity, Barracuda CloudGen Firewall provides a wide range of built-in uplink options including unlimited leased lines, up to twelve DHCP uplinks, and up to four xDSL uplinks. By eliminating the need to purchase additional devices for link balancing, security-conscious customers have access to a WAN connection that never goes down, even if one or two of the existing WAN uplinks are severed. In addition, traffic intelligence mechanisms ensure that the next-defined uplink is activated on the fly and that all traffic is rerouted to make full use of the remaining lines. In the event that backup lines provide less bandwidth, intelligent traffic shaping automatically prioritizes business-critical applications, networks, or distinct endpoints.
Limited network resources make bandwidth prioritization a necessity. Barracuda CloudGen Firewall provides strong Quality of Service (QoS) that lets the administrator apply quality aspects and service guarantees to selected traffic flows within the WAN. QoS is often used to prioritize the network traffic of applications that are critical and must not be affected by the network traffic of other applications.
Barracuda CloudGen Firewall provides a large set of QoS techniques, such as traffic shaping, traffic prioritization, and bandwidth partitioning, which assigns a bandwidth limit to certain types of traffic. To select traffic for different priority classes, the available real-time traffic analysis can be used to identify whether network traffic was sent by business-critical applications or by potentially unwanted applications.
Intelligent Network Perimeters
All Barracuda CloudGen Firewall appliances (virtual editions and cloud versions) include centrally manageable edge computing capabilities based on the Open Container Initiative (OCI) standard. Barracuda CloudGen Firewall treats the edge computing environment as a separate security zone, enabling granular control over all traffic flows and leveraging all next-generation security technologies. CloudGen Firewall enables organizations to run edge-computing apps, process and analyze data at the point of creation and eliminate delays caused by cloud dependencies.
This flexibility supports countless security and non-security applications, making it ideal for distributed sites and remote offices.
Barracuda CloudGen Firewall combines Deep Packet Inspection (DPI) and behavioral traffic analysis to reliably detect and classify thousands of applications and sub-applications, regardless of advanced obfuscation, port hopping techniques, or encryption. It allows the creation of dynamic policies and facilitates establishing and enforcing access and use policies for users and groups by application, application category, location, and time of day. Administrators can now:
Barracuda CloudGen Firewall features advanced application-based routing path selection and Quality of Service (QoS) capabilities. These provide additional business value in addition to security by significantly improving network quality and availability, as well as reducing direct line cost due to bandwidth saved.
For rich reporting and drill-down capabilities, the CloudGen Firewall comes with real-time and historical application visibility that shows application traffic on the corporate network, thus providing a basis for deciding which connections should be given bandwidth prioritization, crucial to QoS optimization for business-critical applications. Furthermore, it allows adjusting and refining the corporate application use policies.
The deep application context analysis allows for deeper inspection of the application data stream by continually evaluating the actual intention of applications and the respective users. Administrators can thereby gain detailed insight into what a specific application was used for or if a user was trying to circumvent the corporate application usage policy.
Barracuda CloudGen Firewall includes true file-type detection and enforcement capabilities based not only on extension and MIME type, but also on sophisticated true file-type detection algorithms. Bypassing executable files by renaming or compressing is detected and blocked. In addition to blocking / allowing connections, the CloudGen Firewall also lets admins change download priorities. If, for example, an ISO image started downloading with normal web traffic priority, the admin can increase or decrease the assigned bandwidth, even though the user started downloading via a regular web-browsing session.
In addition to the thousands of applications pre-loaded in Application Control, Barracuda CloudGen Firewall makes it easy for you to create your own application definitions tailored to your specific needs.
Different network users may need different bandwidth-use rules. Most often, access to certain network resources is limited to certain users or user groups. Preferential allocation of more bandwidth to certain users or user groups and a limitation of available bandwidth for others is a common requirement. It requires the network device to know what user an IP actually belongs to.
Barracuda CloudGen Firewall are fully user-identity aware by linking a user to one or several IP addresses. Any role assignments that result from identity communicated to the firewall by our health agents can be used within the firewall to facilitate role-based access control (RBAC). CloudGen Firewalls support authentication of users and enforcement of user-aware firewall rules, web security gateway settings, and Application Control 2.0 using Active Directory, NTLM, MS CHAP, RADIUS, RSA SecurID, LDAP/LDAPS, TACACS+, as well as authentication with x.509 certificates.
The Web Security Gateway option of the CloudGen Firewall enables highly granular, real-time visibility into online activity broken down by individual users and applications, letting administrators create and enforce effective Internet content and access policies. It protects user productivity, blocks malware downloads and other web-based threats, and enables compliance by blocking access to unwanted websites and servers, providing an important additional layer of security alongside application control.
Every Barracuda CloudGen Firewall includes an Authoritative DNS server to allow intelligent responses to DNS requests by evaluating link state and source IP address before answering the DNS request. This allows e.g. to operate one or multiple web servers or web services protected by Barracuda CloudGen Firewall. By providing different answers to new DNS requests pointing towards alternate servers or links, an efficient server-based load balancing can be implemented without the need for additional hardware or service.
Every Barracuda CloudGen Firewall includes a DNS server to cache and speed up frequently requested DNS requests in the network. The DNS server can function as master, slave, forwarder or a simple cache. The DNS server supports multiple domains as well as DNS doctoring.
Remote Access
Every CloudGen Firewall is a valid enforcement point for Zero Trust Network Access (ZTNA) with SecureEdge Access, making use of the security infrastructure you already have deployed. Simply add additional seats for ZTNA with SecureEdge Access or test out the 10 users that are included with every trial deployment.
The influx of private computing devices, from smartphones to laptops and tablets, into the workplace may help increase productivity, flexibility, and convenience. However, BYOD adds new security challenges and risks, such as enabling and controlling access, as well as preventing data loss.
Barracuda CloudGen Firewall provides strong capabilities to give users the full advantage of their devices while reducing possible risks to the business. Unwanted applications can be blocked, LAN segmentation can protect sensitive data, and network access control can check the health state of each device connecting to the corporate network.
Barracuda CloudGen Firewall incorporates advanced site-to-site and client-to-site VPN capabilities, using both SSL and IPsec protocols to ensure remote users can easily and securely access network resources without complex client configuration and management. Every CloudGen Firewall unit supports an unlimited number of VPN clients at no extra cost.
Barracuda VPN Client also provides the ability to enforce Windows Security Center settings on client machines running Windows. This allows administrators to centrally enforce the usage of Windows Security settings on PCs. The enforced policies can include enabling the Microsoft Network Firewall, Windows Updates, Windows Virus Protection, Windows Spyware Protection, and Internet Security Settings.
Barracuda VPN Clients are available for Microsoft Windows, Mac OS, and various Linux systems.
The optional Advanced Remote Access subscription for Barracuda CloudGen Firewall adds a customizable and easy-to-use portal-based SSL VPN as well as sophisticated Network Access Control (NAC) functionality.
Barracuda Network Access Client, when used with Barracuda CloudGen Firewall, provides centrally managed Network Access Control (NAC) and an advanced personal firewall. This allows enforcement of minimum Windows client security prerequisites before being allowed access to the network or access to a quarantine network. Security posture can be specified according to available Windows patch level, availability of antivirus and/or anti-spyware, and user ID. Access restrictions are enforced locally on the client by the centrally managed personal Windows firewall as well as at the gateway. Using existing Barracuda CloudGen Firewall appliances, Barracuda Networks offers a ready-to-use Network Access Control framework without expensive investments into the basic network infrastructure. All Barracuda Network Access Clients as well as all Barracuda CloudGen Firewall units acting as policy servers can be administered, monitored, and reviewed from a single Barracuda Firewall Control Center.
Gain easy access to your organization’s applications via SSL VPN connections. Barracuda‘s Mobile Portal enables you to set up shortcuts on the home screen of devices such as smartphones or tablets. When accessing the portal via the web browser on a mobile device, users can browse apps, network folders and files as if they were connected to the office network.
The Mobile Portal supports most commonly used devices, e.g., Apple iOS, Android, and Blackberry devices.
Barracuda’s Mobile Portal is an optional feature included with the optional Advanced Remote Access subscription.
CudaLaunch is an application for Windows, macOS, iOS, and Android devices that provides mobile workers secure remote access through Barracuda CloudGen Firewall to their organization’s private cloud applications and other sensitive information. CudaLaunch provides several benefits over traditional browser-based SSL VPN remote access. As an app, it provides a familiar app store setup and install experience for end users.
Unlike browser-based remote access, CudaLaunch provides a more responsive look and feel that is unified across mobile platforms and avoids the idiosyncrasies of mobile browsers. Once an end user starts the app, a swipeable launchpad provides quick and easy access to internal applications, favorites, and TINA VPN connections (which securely connect the device to your corporate network). This richer VPN connection supports mobile apps that connect back to the corporate network (like remote desktop apps).
Designed to be completely self-configuring, CudaLaunch includes easy central management for large deployments and integrates with the powerful security features of Barracuda CloudGen Firewall. For IT administrators, the firewall provides one place to manage security policies for all types of remote access (CudaLaunch, SSL VPN, Barracuda Network Access Client, and standard IPsec). The end user experience is consistent across platforms and remote access types, making for ease of use and significantly lower support costs. The self-configuration and management of VPN connections eliminates the need to manually configure IPsec connections on Windows, macOS, iOS, and Android, making setup fast and easy.
The app is available for free at:
- Mac App Store (macOS)
- Windows Store (Windows)
(Also available as a standalone app that requires no installation; therefore, there are no local admin rights. This version is available on the Barracuda Cloud Control only for windows version.)
App Stores (iOS)
Google Play (Android)
Please note that CudaLaunch requires Barracuda CloudGen Firewall firmware 6.1.1 and an active Advanced Remote Access subscription.
Barracuda Secure Connector appliances are purpose-built ultra-compact edge devices for the Industrial Internet of Things and SoHo use cases. They are designed to provide edge compute capabilities and backhaul all traffic to CloudGen Firewall units (Appliance, Vx or Cloud) or dedicated Secure Access Controllers for scalability. CloudGen Firewall and Secure Access Controller units apply full security inspection.
Management & Automation
Barracuda Firewall Control Center provides 100% central management of all CloudGen Firewall functions, regardless if configuration of security, content, traffic management, networking, access policies or software updates.
Barracuda Firewall Control Center helps reducing the cost associated with security & lifecycle management while providing enhanced troubleshooting and connectivity functionality, both centrally and locally, at the managed gateway.
Barracuda CloudGen Firewalls can automatically translate IP addresses and network addresses to a human-readable format. For example, “EMEA:UK:OXFORD:MARKETING:PRINTER” clearly indicates the location and the device in question at a glance.
Barracuda Firewall Control Center allows you to create re-usable objects for any configuration entry imaginable: IP address, networks, ranges, DNS names, content security policies, network security policies etc.
These objects can be created once and reused in subsequent configurations nodes. For example, if there is an object Internal_Network_Branchname as a network object, it can be referenced in the network settings, firewall rules, and VPN settings. If the object needs to be changed, it only needs to be changed once, preferably on the Firewall Control Center. Then, the changes will be automatically applied at every location where the object is referenced. This provides a faster, easier, and more convenient method of changing configuration services across multiple units.
When configuring multiple CloudGen Firewalls across the WAN, there will always be components that the firewall have in common, such as domain names, DNS servers, NTP servers, application security configurations, URL filter configurations, and so on. Barracuda Firewall Control Center collects all of these in a repository (global configuration node) linked to multiple Barracuda CloudGen Firewalls. Using repositories on the Firewall Control Center, an administrator can update thousands of firewalls with just a single change in the repository.
Repositories still provide the flexibility to override specific settings on specific firewalls. For example, if one location uses a different DNS server than the others, you can create an explicit overwrite for just this setting on this single firewall.
Easily recover firewalls and standalone devices if access is lost for any reason. With the touch of the reset button, the appliance reverts to the last known good state and reconnects to the Firewall Control Center. This effectively removes the need for unplanned visits to remote locations for RMA handling in the event of an error that results in a loss of connectivity.
Barracuda Firewall Control Center provides centralized software updates for all centrally managed CloudGen Firewall units. Updates can be scheduled for a specific time and even just for specific subsets of remote CloudGen Firewall units. In case a software updates is not successful, it is automatically rolled back and reported.
Just like on Barracuda CloudGen Firewall, Barracuda Firewall Control Center allows simultaneous login of multiple administrators in “writing mode”. This is useful in MSSP and multi-admin environments where there is a greater likelihood of administrators managing systems in teams. Once a change needs to be made, only the dedicated configuration node needs to be locked for changing by the admin actually performing the change. All other settings outside of this locked configuration node are still viewable and modifiable by other admins logged on to the system.
Barracuda Firewall Control Center provides extensive role-based administration benefits. Administrators can be assigned specific roles such as: - MSSP Admin - Customer Admin - Log Viewer - Auditor - Content Filter Admin In addition, custom roles for special needs with special privileges can also be created. For example, you can define services to delegate specific tasks to a dedicated team or end user. If one team or end user wants to be able to change firewall rules, a specific customer administrator role can be created that is allowed only to change this particular portion of the configuration. The admin may then review all other configurations, but will not be allowed to change anything else.
Barracuda Firewall Control Center units C610/VC610 and higher provide special handling for multi-tenant management, allowing for a MSSP to be able to easily manage multiple customers on the same Barracuda Firewall Control Center . For example, administrators of Customer 1 will not be able to see anything from Customer 2 and vice versa. There is no limit to how many customers can be administered with one Barracuda Firewall Control Center.
The default screen for every Barracuda Firewall Control Center displays a status overview of all centrally managed Barracuda CloudGen Firewall units. The status is visualized via a traffic light concept (red, yellow, green) and is provided for individual units, clusters, and whole tenant installations (called “Ranges”). The “worst” status always wins, effectively allowing the administrator to have a centralized view of the overall status and to be able to dig deeper with only a few mouse clicks.
Barracuda Firewall Control Center allows the creation of a global firewall ruleset that is installed on all machines it is applied to. In addition, local and special rule sets can be be installed on specific boxes only. For example: The MSSP has a Network Operation Center (NOC) to monitor all services provided to a customer. In this environment, there are global firewall rules that allow every kind of monitoring connection and local firewall rules specific to a customer. The MSSP can determine whether global or local rules take precedent depending on the customer. This provides an added level of granularity for configuration because there are special rules defined for each customer to allow traffic to pass through the firewall. With this feature, the MSSP can be sure that there is a reliable monitoring and log flow. This is required for providing as well as demonstrating proof of service level agreements to customers.
The security landscape just never stop changing. That is why Barracuda Networks constantly introduces and releases new exciting features and improved security functionalities for all its CloudGen Firewalls through its Energize Updates subscription. But when you have dozens or even thousands of devices managed in a company’s WAN network, some devices, networks, or even branches will inevitably run older firmware versions level than certain devices that require the most up-to-date technology. Fortunately, Barracuda Firewall Control Center is backwards compatible to older firmware versions deployed for at least three years, effectively easing the process of needing to upgrade across the organization.
On both Barracuda Firewall Control Center and all Barracuda CloudGen Firewall units, all administrator actions can be logged and changes can be selectively rolled back if required. In case a rollback is required, the administrator has the option to rollback all changes or only specific ones (such as firewall rules) while leaving the network settings untouched.
Barracuda Firewall Control Center VPN Graphical Tunnel Interface (GTI) provides a graphical interface to create and manage VPN tunnels. When configuring VPN tunnels manually, there are many identical configuration steps and settings. But since the GTI Editor eliminates many of these redundant steps, you can configure VPN tunnels more quickly and with less errors.
With a pool license, the license of Barracuda CloudGen Firewall is tied to the Firewall Control Center, not to the serial number and hardware combination. So in case of hardware failure, a new appliance can be deployed without being relicensed. This is great for managed security services providers because they can optimize license usage.
Zero Touch Deployment lets you deploy appliance units directly from the factory to the desired remote location without requiring on-site IT personnel. Simply connect the unit and power it up, and it will automatically select the suitable uplink to the internet and retrieve the appropriate configuration from the Firewall Control Center . With no need for manual configuration on-site, zero-touch deployment allows you to deploy CloudGen Firewalls across widely distributed organizations at very low cost.
Barracuda CloudGen Firewall features a full set of well-documented automation APIs. The Automation APIs included with every CloudGen Firewall allow endusers as well as service partners to automate the management of their devices, across the complete lifecycle. This enables faster deployment, enhanced consistency in management and more rapid adoption of configuration changes for on-premises, virtual as well as cloud-hosted devices.
Enables the API-based management of tens of thousands of firewall devices with new API gateway functionality. One Firewall Control Center is the dedicated API gateway, managing communication and authorization to thousands of child firewall control centers. Each child Firewall Control Center in turn can manage several thousand devices securely, scaling the whole system to tens of thousands of firewall devices.
Reporting
For on-the-fly reporting and drill-down capabilities, Barracuda CloudGen Firewall comes with real-time and historical application visibility that show live and recent application traffic on the corporate network. These can be interactively filtered and drilled down for more details. This helps admins to decide which application connections should be given bandwidth prioritization and who is currently violating acceptable use policies.
Barracuda Firewall Report Creator is a standalone application recommended for reporting on a single appliance or up to few dozen appliances of Barracuda CloudGen Firewall. This free tool creates customized reports using statistics and logs collected directly from the deployed firewalls.
Configuration allows each report to analyze multiple appliances, using custom or predefined report data templates, and a customizable layout and delivery method. Custom reports can include the following information:
- User activity reports – include information on traffic caused by individual users, IP addresses or networks, or active directory user groups.
- Address activity reports – include information for accessed URL categories per source IP address or source network.
- URL category reports – include information on which URLs out of a specific category were accessed based on source IP address or source network.
- Application category reports – include information on detected application categories.
- Application property reports – include information on top blocked or allowed application properties.
- Applications reports – include information on detected applications in a specific application category per source IP address or source network.
- Security reports – include IPS patterns, virus scanner engine, and ATP threat reports.
- VPN usage reports – include information on usage of TINA client-to-site and site-to-site tunnels.
Firewall Report creator is included in the CloudGen Firewall base license.
Barracuda CloudGen Firewall allows leveraging Tufin SecureTrack to view, search and track changes in the corporate security infrastructure, and detect misconfigurations, such as rule permissiveness, shadowing, and more. This vendor-agnostic management platform gives the visibility and control needed to ensure seamless protection, availability of applications and data, and excellent user experience in heterogeneous, multi-vendor, and multi-platform infrastructures.
About Tufin
With over 2,000 customers since its inception, Tufin’s network security automation enables enterprises to implement changes in minutes instead of days, while improving their security posture and business agility.
Use Cases:
Advanced Security
Multi-layered protection against advanced threats.
Protect your organization against today’s sophisticated, evasive threats, thanks to a full stack of advanced capabilities that extend effective security across your entire network.
Remote Access
Optimize productivity for off-network users.
CudaLaunch gives remote users secure access to your company’s applications, network, and data on-premises and in the cloud with zero-touch provisioning.
Cloud Adoption
Migrate securely to SaaS, public cloud, and hybrid environments.
Ensure continuous, secure branch-to-cloud connectivity and application/workload availability as you adopt public-cloud platforms and infrastructures.
Internet of Things
Secure your internet-connected devices and operational technology.
Manage and secure the growing number of internet-connected devices used in your organization and in digital manufacturing processes.
Edge Compute
Moving logic to the point of data creation.
Processing and analysis of data at the point of creation eliminates delays caused by cloud dependencies. This flexibility supports countless security and non-security applications, making it ideal for distributed sites and remote offices.
Zero Trust
Enable Zero Trust using existing firewall infrastructure.
Every CloudGen Firewall is a valid enforcement point for Zero Trust Network Access with SecureEdge Access. Make use of the security infrastructure you already have deployed.
Specifications:
| Barracuda CloudGen Firewall VFC8 | |
|---|---|
| Capacity | |
| Suggested environments | Large businesses |
| Number of IPs | Unlimited |
| Recommended Number of Users | 7,000 |
| Number of CPU Cores Allowed | 8 |
| Features | |
| Firewall incl.IPS | Yes |
| Application Control | Yes |
| Dynamic Routing | Yes |
| App-Based Provider Selection | Yes |
| Remote access | Yes |
| TLS Interception | Yes |
| Secure SD-WAN | Yes |
| Web Filter | Yes |
| Malware Protection | Optional |
| Advanced Threat Protection | Optional |
| Advanced Remote Access | Optional |
| Reporting with Firewall Insights | Optional |
| Premium Support | Optional |
Technical Specs
Firewall
- Stateful packet inspection and forwarding
- Full user-identity awareness
- Intrusion Detection and Prevention System (IDS/IPS)
- Application control and granular application enforcement
- Interception and decryption of SSL/ TLS encrypted applications
- Antivirus and web filtering in single pass mode
- Email security
- SafeSearch enforcement
- Google Accounts Enforcement
- Denial of Service protection (DoS/DDoS)
- Spoofing and flooding protection
- ARP spoofing and trashing protection
- DNS reputation filtering
- NAT (SNAT, DNAT), PAT
- Dynamic rules / timer triggers
- Single object-oriented rule set for routing, bridging, and routed bridging
- Virtual rule test environment
- Network security orchestration with tufin SecureTrack
Hypervisor support
- VMware
- Hyper-V
- KVM
- Proxmox
- XenServer
Protocol Support
- IPv4, IPv6
- BGP/OSPF/RIP
- VoIP (H.323, SIP, SCCP [skinny])
- RPC protocols (ONC-RPC, DCE-RPC)
- 802.1q VLAN
Intrusion Detection & Prevention
- Protection against exploits, threats, and vulnerabilities
- Packet anomaly and fragmentation protection
- Advanced anti-evasion and obfuscation techniques
- Automatic signature updates
Advanced Threat Protection
- Dynamic, on-demand analysis of malware programs (sandboxing)
- Dynamic analysis of documents with embedded exploits (PDF, Office, etc.)
- Detailed forensic analysis
- Botnet and spyware protection
- TypoSquatting and link protection for email
Central Management Options via Barracuda NextGen Control Center
- Administration for unlimited firewalls
- Support for multi-tenancy
- Multi-administrator support & RCS
- Zero-Touch Deployment
- Enterprise/MSP licensing
- Template & repository-based management
- REST API
Infrastructure services
- DHCP server, relay
- SIP and HTTP proxies
- SNMP and IPFIX support
- JSON lifecycle automation API
- Auto VPN via API and script control
- Authoritative DNS server
- DNS server
- DNS Cache
- Built-in support for Azure Virtual WAN
Self-Healing SD-WAN
- Drag & drop configuration
- Optimized direct internet uplink selection
- Internet uplink optimization (forward error correction)
- Simultaneous use of multiple uplinks (transports) per SD-WAN connection
- FIPS 140-2 certified cryptography
- On-demand direct connection creation between remote spoke locations based on application type
- Dynamic bandwidth detection
- Performance-based transport selection
- Application-aware traffic routing
- Adaptive session balancing across multiple uplinks
- Application-based provider selection
- Traffic shaping and QoS
- Built-in data deduplication
Remote and Zero Trust Access
- Network access control
- iOS & Android mobile device support
- Two-factor authentication via timebased one-time passwords (TOTP), Radius, or RSA MFA (requires an active Advanced Remote Access subscription) for remote access clients
- Multi-factor authentication for SSL VPN and CudaLaunch
- ZTNA access and enforcement via Barracuda SecureEdge Access Agents
High Availability
- Active-active or active-passive
- Transparent failover without session loss
- Encrypted HA communication
Support Options
Barracuda Energize Updates
- Standard technical support
- Firmware updates
- IPS signature updates
- Application control definition updates
- Web filter updates
Available Subscriptions
Threat Protection plan
- This subscription plan bundles
- Energize Updates
- Advanced Threat Protection
- Firewall Insights
Total Threat Protection plan
- This subscription plan bundles
- Energize Updates
- Advanced Threat Protection
- Firewall Insights
- Malware Protection
- Advanced Remote Access
Model Comparison:
| Model: | VFC1 | VFC2 | VFC4 | VFC8 | VFC16 | VFC48 | |
|---|---|---|---|---|---|---|---|
| Suggested environments | Homeoffice, Kiosks, IoT/OT | Small & medium businesses | Medium to large businesses | Large businesses | Enterprises | Large enterprises | |
| Allowed cores | 1 | 2 | 4 | 8 | 16 | 48 | |
| Recommended firewall users 2 | 50 | 300 | 2,000 | 7,000 | 10,000 | > 10,000 | |
| Recommended remote access users 3 | 50 | 100 | 250 | 500 | 1,000 | > 1,000 | |
| Optional Features | |||||||
| Standard feature set includes | Firewall incl. IPS, application control, dynamic routing, app-based provider selection, TLS inspection, SD-WAN, web filter | ||||||
| Barracuda Firewall Insights | Optional | Optional | Optional | Optional | Optional | Optional | |
| Malware Protection 4 | Optional | Optional | Optional | Optional | Optional | Optional | |
| Advanced Threat Protection 4 | Optional | Optional | Optional | Optional | Optional | Optional | |
| Advanced Remote Access | Optional | Optional | Optional | Optional | Optional | Optional | |
| Premium Support 5 | Optional | Optional | Optional | Optional | Optional | Optional | |
| Threat Protection plan | Optional | Optional | Optional | Optional | Optional | Optional | |
| Total Threat Protection plan | Optional | Optional | Optional | Optional | Optional | Optional | |
1 All subscriptions mentioned are also available “à la carte”.
2 Protected IP adresses.
3 Depending on hardware specifications.
4 Including FTP, mail and web protocols.
5 Premium Support ensures that an organization’s network is running at its peak performance by providing the highest level of 24x7 technical support for mission-critical environments. For more information, please visit https://www.barracuda.com/support/premium.
Frequently Asked Questions:
Next generation firewalls are the successors of traditional firewall and unified threat management (UTM) devices. Traditional firewalls generally perform packet forwarding and blocking functions and often incorporate packet inspection techniques. UTM devices usually add content security functions but typically fail to tightly integrate those functions tightly with network management, network access and WAN connectivity capabilities of enterprise-class firewalls.
To protect networks in the presence of social media and other Web 2.0 applications, a next generation firewall infrastructure intelligently combines network security, content security, Layer 7 application profiling and network access control to detect application-specific attacks, enforce application-aware inbound and outbound access policies, and perform application-aware traffic routing and prioritization across the wide area network (WAN).
Based on over a decade of R&D and real-world deployments in over 1,000 of the most demanding enterprise customer environments, the Barracuda CloudGen Firewall is the most advanced next generation firewall on the market today.
Network security gateways are the successors of traditional firewalls, unified threat management (UTM) devices, and the latest cycle of "next-generation" firewalls. Traditional firewalls forward packets and block functions often employing packet inspection. UTM devices usually add content security functions. Next-generation firewalls add detection and control of social media and Web 2.0 applications, but typically fail to integrate these functions tightly with link management, WAN management, and SSL VPN remote connectivity.
In comparison, the Barracuda CloudGen Firewall, the first true network security gateway, starts by integrating an advanced network firewall with Layer 7 application recognition and user awareness, content security, malware protection, plus IPS in a suite of security technologies. It tightly integrates these features with intelligent network link aggregation and traffic management, VPN WAN management, and optimization for seamless remote office integration and SSL VPN for remote client security. As a network security gateway, the Barracuda CloudGen Firewall weaves a seamless fabric of security, performance optimization, high-availability, and centralized management into network infrastructures while simplifying network architecture.
As you organization relies on more cloud-based applications like Office 365, Salesforce, and Dropbox, internet connectivity becomes even more important. Our Barracuda CloudGen Firewalls combine powerful application awareness and network routing capabilities to provide the highest levels of internet availability for users and critical applications.
The Barracuda CloudGen Firewall is a next generation firewall and VPN that provides:
- Integrated content security and network access control
- Optimization of intelligent traffic flow across the WAN
- Industry-leading centralized management capabilities
The Barracuda CloudGen Firewall F-Series is designed for network engineers who manage distributed enterprise environments. It provides all the security functionality one expects from an enterprise next-generation firewall, including application detection and prioritization, IPS, malware protection, URL filter and even DDoS protection. Furthermore, its powerful traffic optimization features, extremely resilient site-to-site connectivity capabilities, and extensive logging and auditing tools make the F-series an ideal fit for organizations that need to efficiently manage and scale massive firewall deployments.
The Barracuda CloudGen Firewall S-Series provides remote connectivity in an affordable and easy to deploy solution. It is designed from the ground up to support Internet of Things initiatives where thousands of remote devices need to be connected to a headquarters or data center. The SC appliances are managed via a NextGen Control Center, and security features like IPS, application detection etc. are provided at the Secure Access Concentrator where the VPN for each SC appliance terminates.
The Barracuda CloudGen Firewall X-Series is ideal for small to medium-sized organizations looking for a simple, yet powerful next-generation firewall that provides IPS, application detection, URL filter, malware protection and some basic email security. Designed for the resource-constrained IT professional, the X-Series’ intuitive web interface has a low learning curve while providing and easy-to-use management interface.
If you only have a few locations to manage (e.g., between one and three) and are looking for a firewall that is application aware and easy to use with a Web UI, then the X-Series firewall is ideal for you.
If you have a lot of remote locations to manage, secure and connect (e.g., more than three) and need a solution to seamlessly manage, protect and optimize your network, the F-Series firewall is right for you.
If you have to securely connect large numbers of devices to backhaul traffic to your HQ or data center, want to centrally administer the deployment and stay scalable, then the S-Series is the perfect choice for you.
Yes, all the Barracuda CloudGen Firewall Series—X, F, and S—can be centrally managed from a single pane of glass. The F and S-Series utilize the Barracuda NextGen Control Center to manage massive firewall deployments. The NextGen Control Center is available in physical, virtual and cloud form factors depending on your infrastructure requirements. The X-Series firewall can be centrally managed from Barracuda Cloud Control, which is the same web-based portal that IT administrators use to control their other Barracuda products.
The Barracuda CloudGen Firewall F-Series can easily be deployed as "standalone" and provides great value this way, but its full potential and cost savings is unleashed when it’s centrally managed using a NextGen Control Center.
The S-Series firewall cannot be deployed as standalone, but needs one or multiple Secure Access Concentrators for VPN tunnel termination and a NextGen Control Center for central management. The Web UI on the SC appliances is only intended for initial setup.
The Barracuda CloudGen Firewall X-Series is designed to be used as standalone, and can optionally (at no extra charge) be connected to the Barracuda Cloud Control portal for convenient remote management.
Regardless of whether you’re using the X-Series, F-Series or S-Series firewalls, you can expect the same level of award-winning support from Barracuda’s expertly trained technicians. Barracuda offers 24x7 support with no phone trees, ensuring that you will always speak to an in-region technician who is ready to help.
Barracuda CloudGen Firewall integrates a comprehensive set of next generation firewall technologies, including Web Filtering, malware protection, intrusion prevention, anti-spam protection and Layer 7 application profiling.
Barracuda CloudGen Firewalls include licenses for an unlimited number of IPSec site-to-site connections and IPSec clients through the Barracuda NG VPN Client. The Barracuda CloudGen Firewall SSL VPN and NAC option adds a customizable and easy-to-use Web portal-based SSL VPN as well as sophisticated network access control (NAC) functionality. NAC allows enforcement of minimum Windows client security prerequisites before being allowed access to the network or access to a quarantine network. Security posture can be specified according to available Windows patch level, availability of anti-virus and/or anti-spyware and user ID. The Barracuda NG Network Access Client also adds support for 802.1x port based security for 802.1x enabled routers and switches.
The Barracuda CloudGen Firewall provides application-aware traffic management and prioritization across the WAN, featuring adaptive routing based on network traffic conditions and link status. In addition, through Barracuda NG Control Center, administrators can efficiently monitor VPN tunnels and firewall status.
To centralize management across many different firewalls and remote access users, the Barracuda NG Control Center enables administrators to configure security and network access policies, control firmware update revisions, and manage user settings. Template-based configuration and globally available security objects enable efficient configuration across thousands of locations.
The Barracuda NG Control Center supports multiple administrators simultaneously - even within the same configuration tree. Highly customizable administrative roles can be defined to delegate administrative capabilities for specific departments or locations.
The Barracuda NG Control Center is offered at three levels - Standard Edition, Enterprise Edition and Global Edition. All Barracuda NG Control Center levels enable administration of an unlimited number of Barracuda CloudGen Firewall platforms. The Standard Edition allows for a single configuration group. The Enterprise Edition allows for an unlimited number of configuration groups for a single enterprise / tenant or “range.” The Global Edition is designed for service providers who service multiple tenants and allows for separate and secluded configuration trees for each “range.”
Barracuda CloudGen Firewalls include application layer proxies for HTTP, HTTPS (optional), FTP, SSH, as well as a generic TCP and SOCKS proxy.
Application identification techniques in traditional firewalls typically rely on Layer 3 (destination IP address) or Layer 4 (TCP port / protocol) definitions.
Next-generation firewalls utilizing Layer 7 Application Control can identify and enforce policy on more sophisticated applications that may hide their traffic inside otherwise "safe" port/protocols such as HTTP. Skype and peer-to-peer (P2P) applications are particularly notorious for requiring Layer 7 Application Control for policy enforcement.
The Barracuda CloudGen Firewall integrates Layer 7 Application Control into its core firewall functions, enabling enforcement of policy based on user ID, security policy, location, and time of day. Policy actions can include blocking, allowing, throttling, or even enabling or disabling of specific application features.
The Barracuda CloudGen Firewall can authenticate users and enforce user-aware policy using Active Directory, NTLM, MC CHAP, RADIUS, RSA SecurID, LDAP/LDAPS, TACACS+, built-in local authentication, as well as x.509 certificates.
All Barracuda NG Control Center and Barracuda CloudGen Firewall appliances come with extensive network connectivity troubleshooting and visualization tools. Even for large networks it typically only takes a few mouse clicks to analyze and remediate a problem in the central audit log or access cache screen.
In addition to the Barracuda CloudGen Firewall, Barracuda Networks offers a set of best-of-breed point solutions to address your needs if you are not looking yet to replace your entire firewall infrastructure. Relevant point solutions include:
- Email security: Barracuda Spam & Virus Firewall
- Web filtering: Barracuda Web Filter or Barracuda Purewire Web Security Service
- Layer 7 application profiling: Barracuda Web Filter
- SSL VPN: Barracuda SSL VPN
- Site-to-site IPSec VPN: Barracuda Link Balancer
- Link load balancing: Barracuda Link Balancer
The Barracuda CloudGen Firewall is a family of hardware and virtual appliances designed to service next generation firewall capabilities to all office locations of enterprise networks. This includes very small remote locations, home offices, branch offices, headquarters and data centers. Typically, Barracuda CloudGen Firewall models are sized based on firewall throughput, VPN throughput, concurrent connections, and the features selected. For more information, please contact your Barracuda Networks systems engineer.
No. The Barracuda CloudGen Firewall models include a license to an unlimited number of Barracuda NG VPN clients. With the purchase of the Barracuda SSL VPN and NAC option, there is no licensed limit to the number of Barracuda NG Network Access clients or Barracuda NG SSL VPN users.
Energize Updates from Barracuda Central deliver updates on the extensive library of definitions for intrusion prevention and Layer 7 application profiling. In addition, Energize Updates subscriptions also provide access to Basic Support, Firmware Maintenance and optional participation in the Barracuda Early Release Firmware program.
For additional assistance or for a product demonstration of the Barracuda CloudGen Firewall, please contact us.
Documentation:
Download the Barracuda Networks CloudGen Firewall VFC Virtual Appliance Data Sheet (PDF)
Pricing Notes:
- Please Note: Energize Updates and Instant Replacement Subscriptions need to be maintained for every Barracuda Product. All subscriptions are continuous and must start from the date of activation. Renewals purchases are continuous and start from the date of expiration of your current subscriptions. No exceptions.
- Benefitis of Energize Updates:
- Basic Support, which includes email support 24x7 and phone support between the hours of 9 a.m. and 5 p.m. Monday through Friday in the US (Pacific Time), Japan, China, Austria and the United Kingdom time zones.
- Firmware Maintenance which includes new firmware updates with feature enhancements and bug fixes.
- Security Updates to patch or repair any security vulnerabilities.
- Optional participation in the Barracuda Early Release Firmware program.
- Benefits of Instant Replacement:
- Enhanced Support which provides phone and email support 24x7.
- Data migration service for Barracuda Spam & Virus Firewalls. Barracuda Networks will assist movement of data and configuration from the old product to the new product if the old data is accessible.
- Data recovery service for Barracuda Backup Servers. In the event of a disaster and upon request, Barracuda Networks will preload the most recent data and configuration stored by Barracuda Networks to the new product (note this may take additional time).
- Hard Disk replacement on Barracuda Networks models that have swappable raid drives. Barracuda Networks will ship via standard shipping a hard disk replacement. Customer must return the failed hard disk to Barracuda Networks.
Get a Quote!
Including Energize Update, Advance Threat Protection, and Firewall Insights
List Price:
Our Price: $9,405.00
Including Energize Update, Advance Threat Protection, Firewall Insights, Malware Protection, and Advance Remote Access
List Price:
Our Price: $11,628.00
List Price:
Our Price: $7,524.00
List Price:
Our Price: $923.40
List Price:
Our Price: $1,060.20
List Price:
Our Price: $1,482.00
List Price:
Our Price: $1,824.00
List Price:
Our Price: $1,128.60
Get a Quote!
Get a Quote!
List Price:
Our Price: $8,892.00
List Price:
Our Price: $1,071.60
List Price:
Our Price: $1,368.00
List Price:
Our Price: $1,710.00
List Price:
Our Price: $2,166.00
List Price:
Our Price: $1,368.00