Barracuda Managed XDR & SOC
Stay ahead of attackers with 24/7 managed cybersecurity.
Sorry, this product is no longer available, please contact us for a replacement.
Overview:
Cover the blind spots in your cybersecurity.
Cyberattacks can reach your organization from any device and attack surface. With limited cybersecurity resources, how do you keep up with the ever-increasing volume of sophisticated, AI-powered attacks?
95%
increase in global ransomware attacks over 2022.1
1. 2023 Q3 Corvus Insurance Ransomware Report71%
of organizations are impacted by cybersecurity skills shortage.2
2. The Life and Times of Cybersecurity ProfessionalsGet extended detection and response (XDR)
combined with our award-winning security
operations center (SOC).

Accelerate threat detection
Are threat actors in your systems right now? Kick attackers out before they can monitor, damage or steal from your business.

Protect all attack surfaces
Today’s cyber criminals are smarter and attacks are more complex. Actively monitor your entire environment for ultimate protection.

Augment your limited IT resources
Hiring and retaining specialized cybersecurity talent is harder than ever. Simplify your operations with our unified platform and SOC.
XDR at a glance
X
Extend your protection to endpoint devices, cloud, email, and servers.
D
Automatically detect billions of raw events from 40+ integrated data sources, including sophisticated attacks like account takeover and ransomware.
R
Respond to each threat with our automated prescriptive instructions, automation, and Barracuda’s 24/7 award-winning Security Operations Center.
Accelerate detection and response
from months to hours.
With our extensive threat detection rules that map to the MITRE ATT&CK® framework, Barracuda Managed
XDR can detect threats earlier and help you respond to threats faster. With Barracuda Managed XDR,
malware infection resolution can be reduced from 3-4 weeks to less than one hour.
Typical response times to advanced cyberattacks.

Without XDR

With XDR
Business email compromise resolution (gateway only)
1–2 months
1–2 hours
Malware infection resolution
3–4 weeks
1 hour
Extortion resolution
Varies
Under 24 hours
Fully protect your business across
multiple attack surfaces.
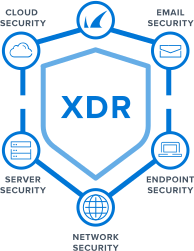
Attacks can come from anywhere.
Most attacks begin with malicious email, infect your endpoint, and then work quickly to gain access to your network. Accurate and fast detection is crucial. However, most organizations lack the visibility into such attacks and the capacity to detect and respond effectively. Managed XDR provides that visibility and automates the detection and response to thwart attacks early, when it matters the most.
Contain and disrupt cybercriminals.
Stand up to threat actors and protect your organization from cyberthreats. Perform containment and remediation steps more quickly utilizing automation. Use of rules, an AI-powered analytics engine, and intervention by the SOC enables automatic remediation and containment actions.
Achieve essential cyber hygiene.
Reduce cyber risk by rapidly strengthening your security posture and meeting compliance and cyber insurance requirements. Retaining and monitoring security logs is usually required to comply with compliance frameworks and industry standards. Most cyber insurance policies also require you to have adequate endpoint detection (EDR) with Managed XDR.
- Meet cyber insurance requirements
- Ensure regulatory compliance
- Keep users and data protected
Don’t let threats go undetected.
Barracuda XDR detects thousands of threats with the latest threat intelligence and AI.
With endpoint protection, Barracuda can identify and rollback ransomware attacks from endpoint devices.
Track when a user is added to a high-risk security group.
Get alerted when a user’s IP address suspiciously changes countries in a short period of time.
Credential theft can lead to data exfiltration and account takeover. Barracuda XDR alerts you to attempts to break into your systems.
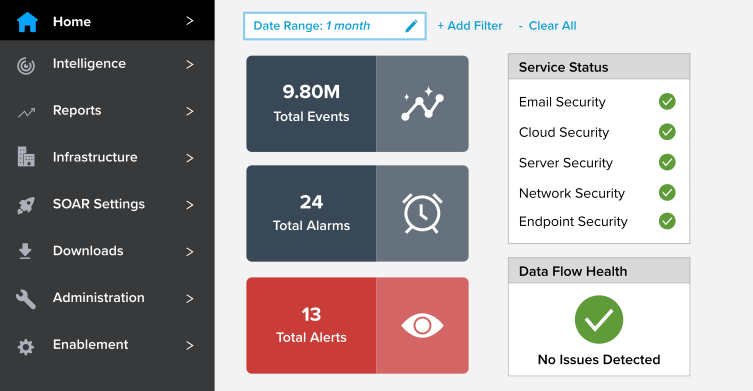
Threats can come from multiple attack vectors. XDR monitors thousands of events and corelates the threats to provide visibility, detection and response.
Our 24x7 Security Operations Center extends your cybersecurity team.
In addition to a unified SOC platform, instantly augment your internal resources with teams of tenured security experts. This combination of human-intelligence, artificial intelligence (AI), and an innovative SOC platform efficiently and effectively detects and triages incidents and provides you with enriched alerts and prescriptive recommendations to resolve incidents promptly.
Our multi-tiered global SOC, consisting of seasoned teams of security analysts and engineers, is structured to provide 24x7x365 service with a follow-the-sun strategy for protection at all times, regardless of your location.
Features:
Managed XDR Suite
Real-time threat monitoring and guidance from security experts are divided into dedicated teams for around-the-clock coverage. Each security operations center (SOC) team works in the background to provide proactive detection and response services to you. The SOC teams continually research and develop new security detections, ensuring Barracuda XDR stays ahead of the ever-evolving cyberthreat landscape. Direct access to the SOC is available with one phone number.
Regional data residency is available in North America, Europe, Middle East, Africa, and Asia-Pacific.
Centralized and correlated attack telemetry across endpoints, servers, networks, cloud services, and email reduces complexity and improves visibility compared to monitoring disparate systems. It also allows for the detection of patterns or anomalies that might not be apparent when looking at individual logs.
Enhances threat detection and response by offering a complete perspective and relevant context. This includes asset data, threat intelligence data, and user information, enabling analysts to prioritize and investigate threats more efficiently. The added information facilitates a better understanding of the significance of events, leading to faster investigations and more effective automation.
Provides security incident and event management (SIEM), security orchestration, automation, and response (SOAR), threat intelligence platform (TIP), and incident management system (IMS) functionality in a single platform.
Go beyond the traditional visibility triad of endpoint, network, and logs. This cloud-native cybersecurity platform offers a single-pane-of-glass view of additional telemetry throughout your environment. The Barracuda XDR platform also analyzes data from existing security solutions to provide centralized visibility.
Build layers of security around your data, devices, and users. Multiple security layers are necessary in order to provide the protection your organization needs. Barracuda XDR adds additional layers of protection for major attack surfaces such as email, endpoints, servers, firewalls, and cloud devices.
The growing list of technology integrations allows the Barracuda XDR teams to monitor commonly requested data sources. Proprietary detections are powered by machine learning (ML) and are mapped to the MITRE ATT&CK® framework, allowing Barracuda XDR to detect threat actors faster and predict their next move.
Barracuda utilizes a large global threat indicator repository informed by rich security intelligence feeds from diverse sources with over 11 billion indicators of compromise (IOCs), including Barracuda's proprietary intelligence, to help customers against new and emerging threats.
XDR Endpoint Security
Looks for suspicious or malicious activity by monitoring and analyzing the events and actions on specific hosts, such as workstations or servers. By analyzing system logs, file integrity, and processes, it focuses on finding possible threats and abnormalities inside the host environment.
Detect ransomware execution, application misuse, privilege escalation, crypto mining, remote code execution, command shell activity, and fileless attacks.
Monitor and correlate all endpoint activities, including processes, files, and network connections, to detect complex threats like zero-day assaults that bypass standard security. By investigating anomalous behaviors or abnormalities in the environment, the SOC can find dormant or hidden threats.
Quickly understand the scope and impact of an incident by providing detailed investigation data, including a timeline of events, which helps determine how an attack occurred and what assets were affected. This detailed information allows for faster and more precise remediation actions, reducing the time an attacker has to cause damage.
Automatically responds by isolating affected endpoints and terminating malicious processes, mitigating threats quickly without relying solely on manual intervention.
Automate responses to common threats or suspicious activities, reducing the burden on security teams. This automation can lead to faster incident response times and allow teams to focus on more complex tasks. Detect threats that are unique to your environment or industry. Ensure that security policies are applied consistently across the organization to reduce the risk of human error and ensure that the organization's security posture remains robust.
Quickly revert systems to a state before an attack occurs, including file-based and file-less malware that operates in memory or alters system processes. This minimizes downtime and data loss, negating the impact of the attack without needing to resort to backups or manual data recovery processes. This helps security teams respond more efficiently and return systems to normal operation quickly.
Ensures that the agent has the latest threat intelligence and detection algorithms to accurately identify and respond to the newest malware, ransomware, and other threats.
XDR Network Security
Detects a variety of network-based threats, such as malware, intrusions, and abnormalities, by conducting comprehensive multi-protocol analysis (e.g., HTTP, HTTPS, DNS, and FTP) in real time. It offers extensive visibility into network activity by examining every packet of traffic on the network. This is essential for spotting odd behaviors or trends that can point to a security compromise.
Detect malicious network activity such as denial-of-service attacks, data leaks, unauthorized changes, IDS-based signatures, and brute-force attacks.
Through the use of API, threats are automatically contained by blocking malicious traffic (IP addresses) in supported firewalls. This reduces the time it takes to mitigate threats via automation, reducing the time a threat remains active and minimizing potential damage.
XDR Cloud Security
Monitor multiple cloud services for malicious activity to identify identity, privilege, and MFA fatigue attacks in identity solutions, including AWS CloudTrail and GuardDuty, Duo, Google Workspace, Microsoft 365 and Azure, Okta, and more.
Detect malicious activity in the cloud such as account takeover, suspicious login, MFA disabled, data authentication bypass, admin changes in the environment, impossible logins, inbox rules, and unauthorized access to cloud mailboxes and infrastructure.
XDR Server Security
Reveals unusual patterns of behavior, which can indicate the presence of malware, insider threats, or external attacks. Early detection allows for quick responses before they escalate into serious incidents.
Multiple Windows user account lockout, rare user login, Kerberos password spray attempt, Impacket PsExec reverse shell executed, encrypting files with WinRAR or 7z, new domain admin created.
Identifies unauthorized access attempts, successful abnormal account lockouts, compromised user accounts, privilege escalation attempts, creation or deletion of user accounts, and monitors changes made to group policies. Detects unusual login activities across multiple systems, indicating potential lateral movement by an attacker. It helps in detecting potential insider threats or attackers trying to establish persistence.
XDR Email Security
Shows which users are being targeted by phishing campaigns, enabling targeted awareness training and preventative measures. Provides visibility into the types of attachments being sent and received. Detects the unauthorized sending of sensitive information (such as financial data, personal information, or intellectual property) outside the organization. Helps in preventing data breaches and maintaining regulatory compliance.
Inbound attachment detained, policy deleted by administrator, malicious URL not blocked, potential data exfiltration.
Integrates with Barracuda, Mimecast, Defender for Office 365, and other cloud email infrastructure to monitor and provide additional analysis of potential email risks.
Documentation:
Download the Barracuda Networks Managed XDR Data Sheet (PDF)
Download the Barracuda Networks Managed XDR Endpoint Security Data Sheet (PDF)
Download the Barracuda Networks Managed XDR Cloud Security Data Sheet (PDF)
Download the Barracuda Networks Managed XDR Network Security Data Sheet (PDF)
Download the Barracuda Networks Managed XDR Server Security Data Sheet (PDF)
Download the Barracuda Networks Managed XDR Email Security Data Sheet (PDF)